Learn SQL injection by flying to Mars in Pathfinder
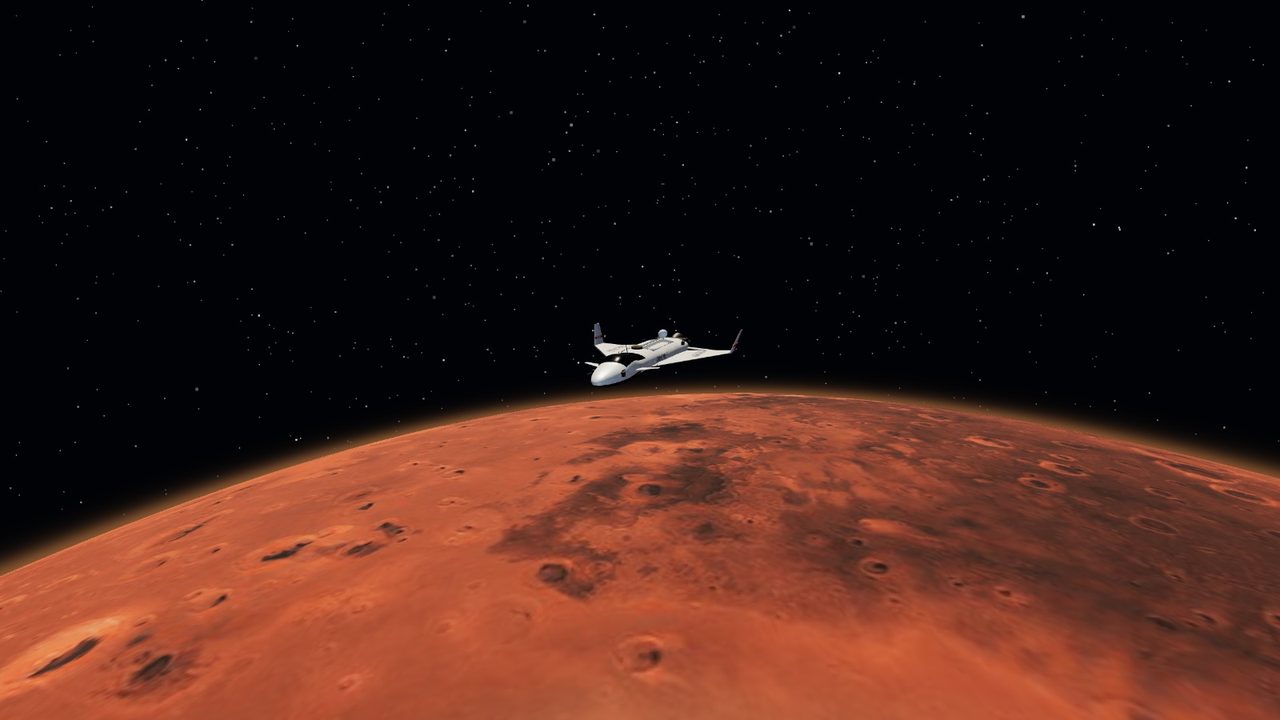
Fly the PATHFINDER spaceplane to Mars and explore its surface. After 60 seconds the flight computer locks and asks for a licence key you don't have. The key is in Mission Control's systems. To keep flying, you have to break in and find it.
It is a hands-on way to learn SQL injection, one of the most common web vulnerabilities in the real world. And the geography of Mars.
The physics, simply
- Mars is smaller than Earth. Its gravity is about 38% of ours. If you weigh 40 kg on Earth, you would feel like 15 kg on Mars.
- The air is very thin. Less than 1% of Earth's. Wings and parachutes help much less there, so engines do most of the work.
- Orbit is falling sideways. In orbit you are falling all the time, but you are moving sideways so fast that you keep missing the ground. Slow down and you start coming down.
- Look around. The surface is built from real Mars maps. Find the giant volcanoes and the huge canyons.
A small hint
Talk to the database. The crew roster in the game asks a database for names. What happens if you give it something that is not a name? And once you have some passwords, remember that some are much weaker than others.
Why this matters
SQL injection has been around for more than 25 years and it still breaks real websites. One search box that trusts what you type can leak a whole user table. Weak passwords make it worse. If you understand this one bug well, you understand a lot about web security.
Don't want to hack? There is a free play mode too. Just fly.
CyberLearner.org is a free cybersecurity training platform, built on the curriculum of the International Cybersecurity Olympiad (ICO). Every lab is hands-on and runs in your browser. It is open to everyone, regardless of skill level.